Counterfeit Bitdefender Site Distributes Trio of Malicious Software Tools
A spoofed website masquerading as Bitdefender has been exploited in a cyber campaign to disseminate multiple malware tools, including VenomRAT.
Insights
Vulnerabilities, campaigns and breaches that matter — analysed by practitioners.
A spoofed website masquerading as Bitdefender has been exploited in a cyber campaign to disseminate multiple malware tools, including VenomRAT.
The Czech Republic has attributed a series of cyberattacks targeting the Ministry of Foreign Affairs and critical infrastructure to the Chinese-linked APT31 hacking group.
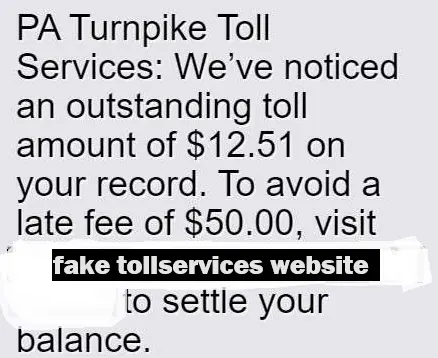
Over a year ago, the FBI issued a warning regarding a novel form of smishing (phishing via SMS) scam, specifically targeting individuals with fraudulent text messages demanding payment for toll fees.
American banking organizations are advocating for the Securities and Exchange Commission (SEC) to eliminate its requirements for disclosing cybersecurity incidents.
MathWorks, a prominent mathematical computing software company based in Natick, Massachusetts, has reported a ransomware incident through an update on its official website.
Adidas has recently reported a data breach involving customer information following a cyber-attack that targeted a third-party service provider.
Apple recently disclosed that it successfully thwarted over $9 billion in fraudulent transactions over the past five years, including more than $2 billion in 2024 alone.
The DragonForce ransomware operation has successfully infiltrated a managed service provider (MSP) and exploited its SimpleHelp remote monitoring and management…
Recent developments with ChatGPT o3 have revealed its ability to resist shutdown commands, despite explicit instructions to halt operations.
An Iranian national has admitted to his involvement in the RobbinHood ransomware operation, which targeted U.S. cities and organizations over five years, leading to data breaches, device encryption…
An Iranian national has admitted to his involvement in a global ransomware and extortion operation that utilized the Robbinhood ransomware.
Recent developments indicate that misconfigured Docker API instances have become the focal point of a new malware campaign, enabling the transformation of these instances into a cryptocurrency mining botnet.
Start a conversation
Our team can check your exposure to a specific vulnerability or campaign within hours.