UN Introduces Comprehensive Cyber-Attack Assessment Framework
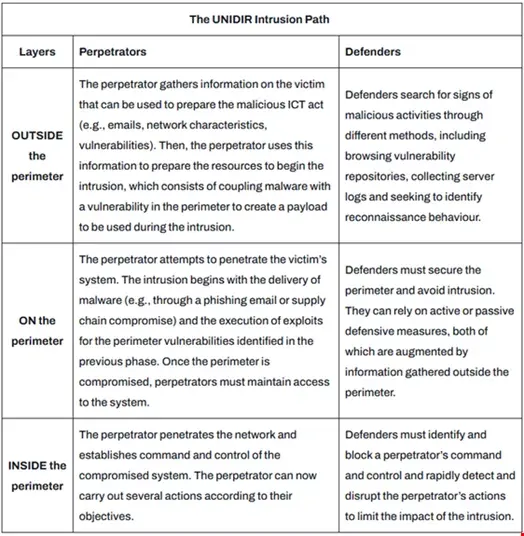
The United Nations has introduced a new cyber-attack assessment framework to complement existing cybersecurity models like the MITRE ATT&CK framework.
Insights
Vulnerabilities, campaigns and breaches that matter — analysed by practitioners.
The United Nations has introduced a new cyber-attack assessment framework to complement existing cybersecurity models like the MITRE ATT&CK framework.
The reactive nature of vulnerability management, along with the delays introduced by policy and process constraints, places considerable strain on security teams.
Edge devices, particularly routers that no longer receive security updates, have become prime targets for cyber threat actors.
Education technology provider PowerSchool has confirmed that it paid a ransomware demand to prevent cybercriminals from publishing stolen data belonging to teachers and students in the US and Canada.
Google has announced the rollout of new artificial intelligence (AI)-powered measures designed to combat scams across its platforms, specifically Chrome, Search, and Android.
A China-linked threat actor known as Chaya_004 has been identified exploiting a recently disclosed vulnerability in SAP NetWeaver.
The FBI has issued a warning regarding the exploitation of end-of-life (EoL) routers by threat actors who deploy malware to transform these devices into proxies for sale on the 5Socks and Anyproxy networks.
Cloud-native applications provide significant advantages, including scalable and automated workflows, enhanced data processing capabilities, and efficient deployment mechanisms.
Cisco has addressed a high-severity vulnerability in IOS XE Software affecting Wireless LAN Controllers.
Education provider Pearson has been compromised in a recent cyberattack that has exposed sensitive corporate and customer data.
In response to a significant data breach, PowerSchool has opted to meet the demands of ransomware perpetrators.
An npm package, 'rand-user-agent', has been affected by a supply chain attack that resulted in the injection of obfuscated code designed to activate a remote access trojan (RAT) on users' systems.
Start a conversation
Our team can check your exposure to a specific vulnerability or campaign within hours.