Ahold Delhaize Reports Data Breach Impacting 2.2 Million Individuals
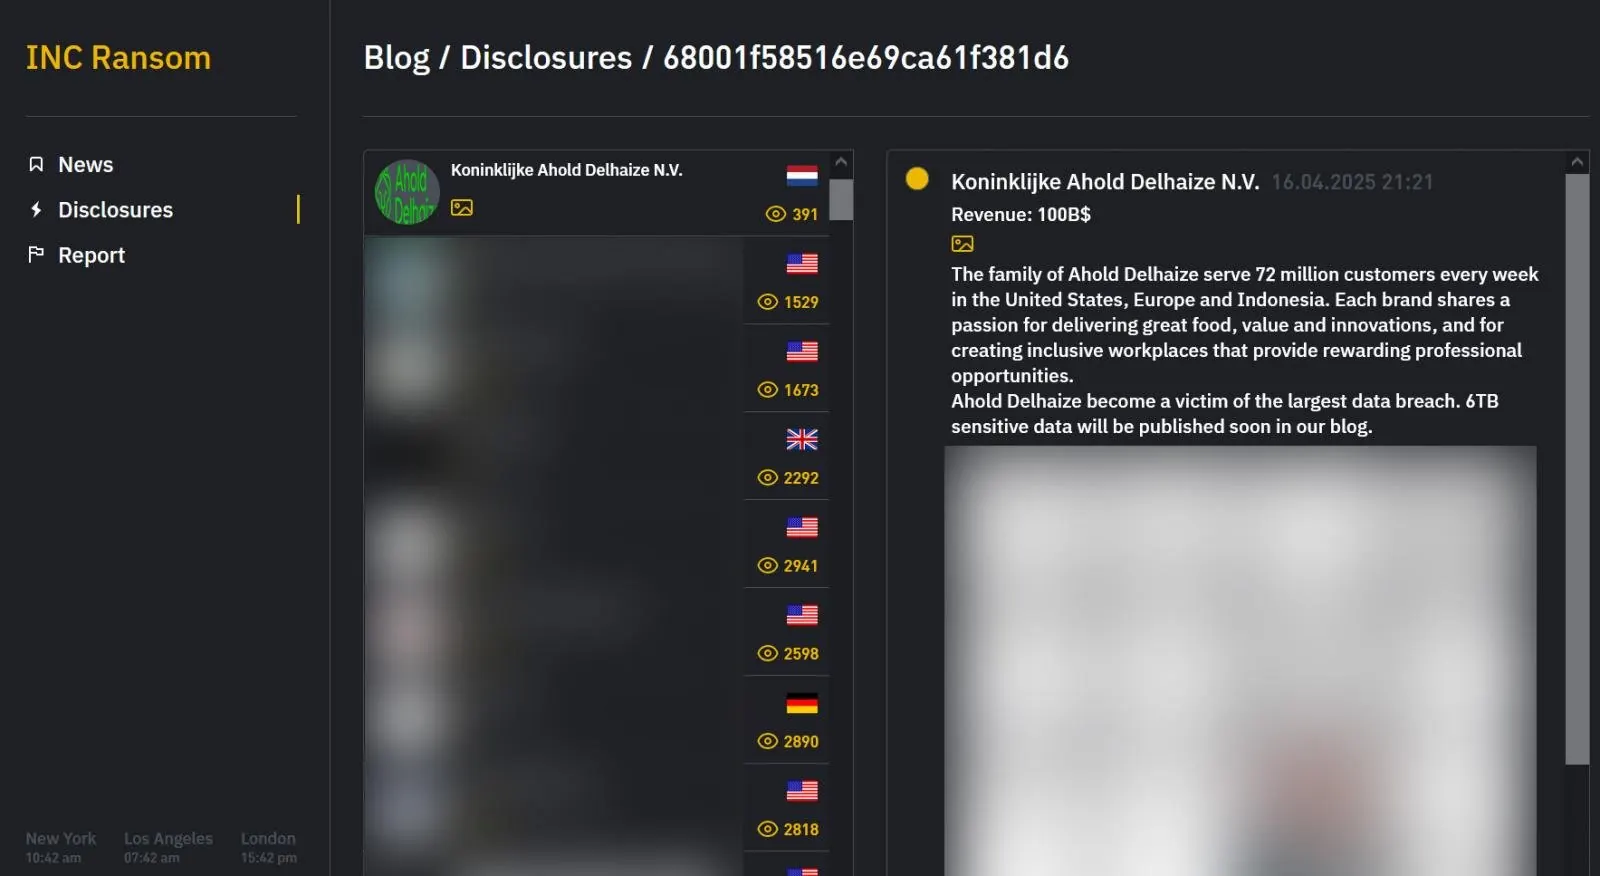
Ahold Delhaize, a prominent global food retail chain, has alerted over 2.2 million individuals regarding the unauthorized access and theft of their personal, financial…
Insights
Vulnerabilities, campaigns and breaches that matter — analysed by practitioners.
Ahold Delhaize, a prominent global food retail chain, has alerted over 2.2 million individuals regarding the unauthorized access and theft of their personal, financial…
A significant rise in scanning activity targeting MOVEit Transfer systems has been detected, indicating a potential surge in attacks against the software.
Threat intelligence firm GreyNoise has reported a significant increase in scanning activity targeting Progress MOVEit Transfer systems, which began on May 27, 2025.
Microsoft has released the KB5060829 preview cumulative update for Windows 11 24H2, introducing a total of 38 enhancements, including notable improvements to the taskbar and a new PC-to-PC migration experience.
United Natural Foods, Inc. (UNFI), a prominent grocery wholesaler and key distributor for Whole Foods, has successfully restored its core operational systems following a recent cyberattack.
Hawaiian Airlines, one of the largest commercial carriers in the United States, is actively investigating a cyberattack that has resulted in limited disruptions to its internal systems.
The Federal Bureau of Investigation (FBI) conducted a thorough investigation into the activities of IntelBroker, a prominent figure operating under the alias Kai West in the United Kingdom.
The Federal Trade Commission (FTC) has sanctioned $126 million in refunds to be disbursed to 969,173 Fortnite players…
Cybersecurity researchers have identified a significant vulnerability in the Open VSX Registry (open-vsx.org), which, if successfully exploited…
A growing number of Model Context Protocol (MCP) servers, which are linked to artificial intelligence, have been identified as misconfigured and vulnerable to significant security threats.
Cisco has issued a security advisory regarding two critical, unauthenticated remote code execution (RCE) vulnerabilities affecting the Cisco Identity Services Engine (ISE) and the Passive Identity Connector (ISE-PIC).
A patient’s death has been officially attributed to the ransomware attack on Synnovis, the pathology services provider for multiple NHS hospitals in London, which occurred in 2024.
Start a conversation
Our team can check your exposure to a specific vulnerability or campaign within hours.